Resume template · Updated October 2026
Penetration tester resume template
Short answer
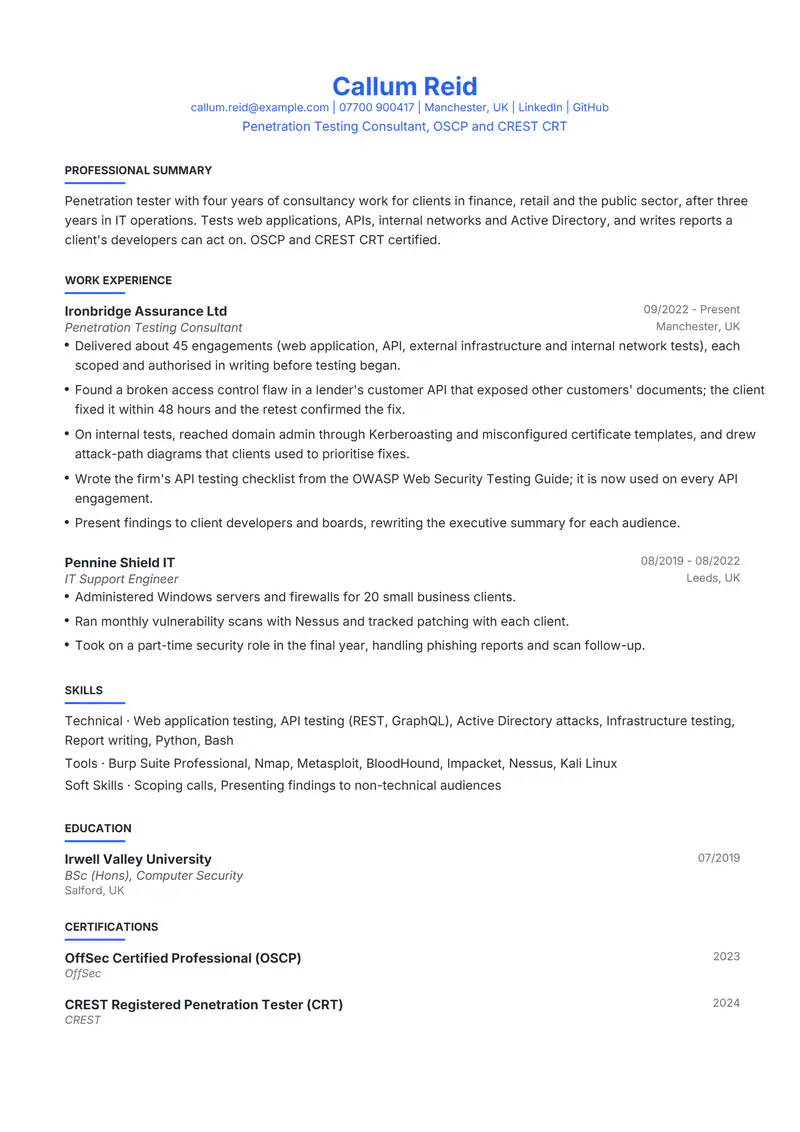
Leslie suits a penetration tester because it prints engagements and findings straight after the summary, ahead of a tool list that looks much the same on every tester's page. The fictional sample is a penetration testing consultant in Manchester with four years of client work after three in IT operations: web, API and Active Directory tests, findings told as attack paths, a disclosed CVE, and OSCP and CREST CRT in the headline.
Download the penetration tester sample
Callum is a fictional penetration testing consultant. Replace every detail with your own before you send it.
The files are made in your browser by Resumity's own exporters, from this sample. The builder opens it as your own resume: click any line to replace it. Free plan, no watermark.
Why Leslie suits a penetration tester resume
Leslie prints work experience before skills. Most testers list the same toolset (Burp Suite, Nmap, Metasploit, BloodHound), so the engagements, findings and reports are what set one candidate apart, and Leslie puts them directly under the summary. The centred blue header is its single touch of colour, which keeps a consultancy CV sober.
Second choice: Catalyst. Catalyst opens on the current job with a large left-aligned name and no summary; pick it when your certifications sit in the headline and the engagements need no introduction.
What goes in each section, in Leslie's order
Leslie prints its sections in a fixed order, the same in the PDF and the Word file. Here is that order for this sample, and what to put in each section.
- Professional Summary. State what you test (web, API, infrastructure, Active Directory, cloud), for whom (sectors, consultancy or in-house) and your certifications. Leslie prints certifications near the bottom, so OSCP and CRT belong in the headline and summary too.
- Work Experience. Count engagements by type, then pick two or three findings told as impact: what an attacker could reach, how you demonstrated it, what the client changed. Say that testing was scoped and authorised in writing; it tells a hiring manager you work like a professional.
- Skills. Testing areas in Technical, named tools in Tools, client-facing skills in Soft Skills. Include the scripting language you use for custom tooling, because technical interviews often ask you to read or adapt a short exploit script.
- Education. Degree, subject and year on one line. If you came through IT operations or development instead, the experience section already shows the route.
- Certifications. OffSec awards OSCP after a 24-hour proctored exam against live machines, including an Active Directory set; CREST CRT is a practical exam that needs a valid CPSA before you can book it. Write each full name with the year so a reader can check it.
- CVEs and research. The sample calls this "CVEs and research": a responsible disclosure and a talk at a local chapter meeting. Only public, disclosed work goes here, never a client finding.
The sample resume as text
The same content as the files above, so you can copy a line or compare it with your own.
Callum Reid
Penetration Testing Consultant, OSCP and CREST CRT
Manchester, UK | callum.reid@example.com | 07700 900417 | linkedin.com/in/sample-callum-reid | github.com/sample-callum-reid
Penetration tester with four years of consultancy work for clients in finance, retail and the public sector, after three years in IT operations. Tests web applications, APIs, internal networks and Active Directory, and writes reports a client's developers can act on. OSCP and CREST CRT certified.
Experience
Penetration Testing Consultant, Ironbridge Assurance Ltd, Manchester, UK (09/2022 to Present)
- Delivered about 45 engagements (web application, API, external infrastructure and internal network tests), each scoped and authorised in writing before testing began.
- Found a broken access control flaw in a lender's customer API that exposed other customers' documents; the client fixed it within 48 hours and the retest confirmed the fix.
- On internal tests, reached domain admin through Kerberoasting and misconfigured certificate templates, and drew attack-path diagrams that clients used to prioritise fixes.
- Wrote the firm's API testing checklist from the OWASP Web Security Testing Guide; it is now used on every API engagement.
- Present findings to client developers and boards, rewriting the executive summary for each audience.
IT Support Engineer, Pennine Shield IT, Leeds, UK (08/2019 to 08/2022)
- Administered Windows servers and firewalls for 20 small business clients.
- Ran monthly vulnerability scans with Nessus and tracked patching with each client.
- Took on a part-time security role in the final year, handling phishing reports and scan follow-up.
CVEs and research
- CVE assigned for a stored cross-site scripting flaw in an open-source helpdesk application, reported to the maintainer and fixed in the next release.
- Talk at a local OWASP chapter meeting on testing GraphQL APIs.
Education
BSc (Hons), Computer Security, Irwell Valley University (07/2019)
Certifications
- OffSec Certified Professional (OSCP), OffSec (2023)
- CREST Registered Penetration Tester (CRT), CREST (2024)
Skills
Web application testing, API testing (REST, GraphQL), Active Directory attacks, Infrastructure testing, Report writing, Python, Bash, Burp Suite Professional, Nmap, Metasploit, BloodHound, Impacket, Nessus, Kali Linux, Scoping calls, Presenting findings to non-technical audiences
How to make the sample yours
Change the sector mix to yours
Finance, retail, public sector, healthcare: the sectors you have tested tell a consultancy which clients it could put you in front of in your first week.
Rewrite one finding as an attack path
Start where you began (an unauthenticated API, a standard domain user) and end at what you reached (another customer's documents, domain admin). Then add the fix the client made.
Keep the authorisation wording
"Scoped and authorised in writing before testing began" is one clause, and it answers a question every hiring manager has about a tester's judgement.
Show report-writing evidence
A checklist you wrote, a report template you improved, a board presentation. Clients pay for the report as much as for the testing.
Remove anything a client could recognise
Sector and size are fine; client names, product names and details of unpatched findings are not, even if the engagement ended years ago.
Keywords to keep where they are true
Terms this kind of resume is usually searched for. Use the posting's exact wording, and only for work you have done.
- penetration testing
- web application testing
- API security testing
- internal infrastructure testing
- Active Directory
- Burp Suite
- Nmap
- Metasploit
- BloodHound
- OWASP WSTG
- OWASP Top 10
- privilege escalation
- report writing
- OSCP
- CREST CRT
Mistakes to avoid
- Client names, or findings described in enough detail to identify the client.
- Capture-the-flag rankings presented as client engagements.
- Any hint of testing without permission, including bug bounty work outside a program's scope.
- A long tool list with no findings attached. Anyone can install Kali Linux.
How the sample PDF reads in text extractors
We exported this sample with Resumity's PDF exporter in Chrome on 2026-10-29 and read the file back with three open-source text extractors. This shows whether software that turns a PDF into text can recover it; it is not a test of any commercial applicant tracking system. How we test templates.
| Extractor | Name, email, phone | Headings | Bullets intact |
|---|---|---|---|
| pdf.js 4.10.38 | All found | 6 of 6 | 8 of 8 |
| pdftotext (Xpdf) 4.00 | All found | 6 of 6 | 8 of 8 |
| pypdf 6.13.0 | All found | 6 of 6 | 8 of 8 |
Frequently asked questions
Should I list both OSCP and CREST certifications?
Yes, if you hold both; they test differently. OSCP is a 24-hour hands-on exam, while CREST CRT is a shorter practical exam taken in a Kali environment CREST provides. OffSec now awards OSCP+ alongside OSCP, and the OSCP+ designation expires after three years, so give the year.
How do I describe findings without breaking client confidentiality?
Use the sector, the type of system and the class of flaw, as in "broken access control in a lender's customer API". Leave out client names, URLs and anything still unpatched, and check your employer's rules before you write.
Do CTF and lab results belong on a penetration tester resume?
Early on, yes, in a clearly labelled list: lab completions, CTF placings, write-ups you published. Once you have client engagements, keep only the strongest one or two.
How do I move from IT support or a SOC into penetration testing?
Show the security work in your current job (scans, phishing triage, hardening), add a certification such as OSCP, and publish something: a write-up, a tool, a disclosed bug. The older job in the sample shows that route.
Is a penetration testing consultant resume different from an in-house tester's?
Consultants should show breadth (engagement count, sectors, test types) and client communication. In-house testers do better showing depth in one estate: repeat testing, fixes verified, security built into releases.
Will applicant tracking systems read this Leslie PDF?
The sample PDF read back with its contact details, all 6 section headings and all 8 bullets intact in three open-source text extractors (pdf.js, pdftotext and pypdf). Commercial systems such as Workday, Greenhouse or Taleo were not tested, and each employer configures its own.
Guides and templates for this resume
Sources, checked 29 October 2026
We opened every page below on that date. Pay, rules and requirements change, so check the source before you rely on a detail.
- OffSec: PEN-200: Penetration Testing with Kali Linux (OSCP) (the exam is 24 hours, proctored, against live machines including an Active Directory set; passing gives OSCP and OSCP+, and OSCP+ expires after three years)
- CREST: CREST Registered Penetration Tester (CRT) (practical exam of 2.5 hours in a CREST-provided Kali environment; a valid CPSA is required before booking)
- OWASP Foundation: OWASP Web Security Testing Guide (testing guide for web application security; latest stable version 4.2)
More in resume templates by job title.