Resume template · Updated October 2026
Security engineer resume template
Short answer
Pick FAANGPath for a security engineer at a product company: the skills block sits above the jobs, so a reader sees that you write Python and Go and know AWS IAM before reaching the first role. The fictional sample spent eight years in application and cloud security, now at a telehealth company, building scanning into CI, removing long-lived keys and running threat models with product engineers. CISSP is in the headline.
Download the security engineer sample
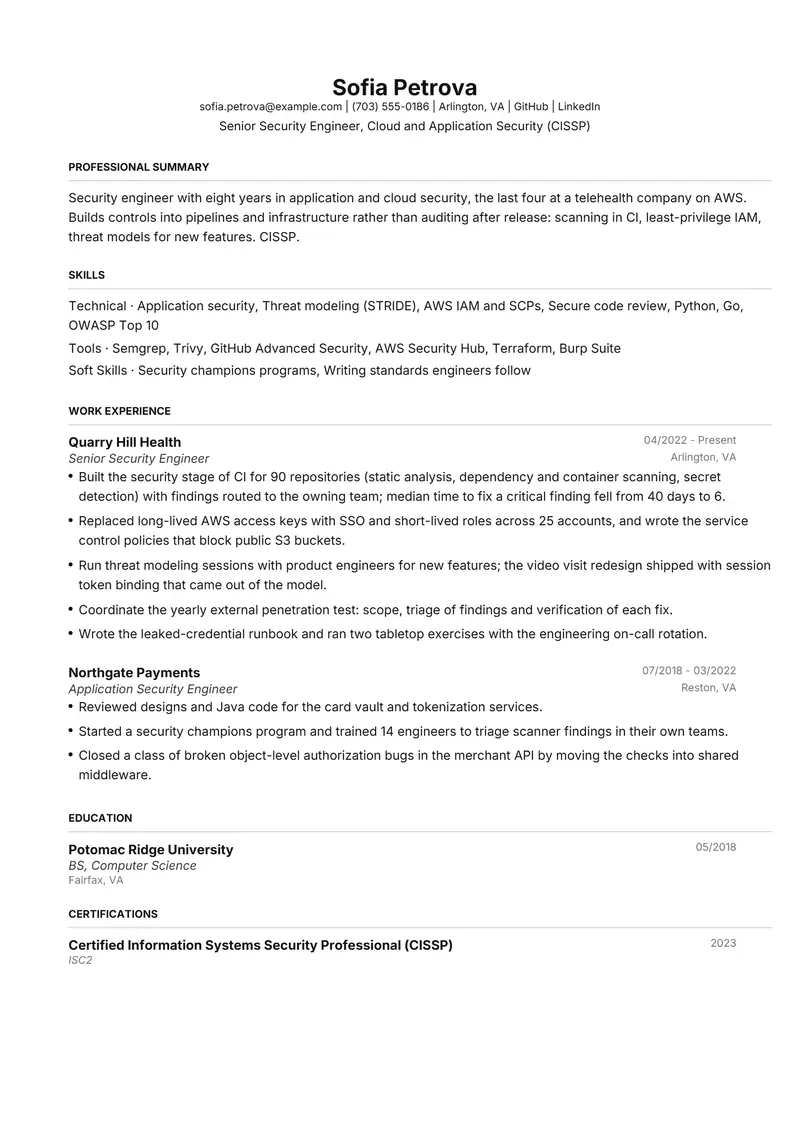
Sofia is a fictional senior security engineer. Replace every detail with your own before you send it.
The files are made in your browser by Resumity's own exporters, from this sample. The builder opens it as your own resume: click any line to replace it. Free plan, no watermark.
Why FAANGPath suits a security engineer resume
FAANGPath was drawn for technical candidates and prints labelled skill rows, a dot after each label, ahead of experience. Security engineers who build controls are screened first on whether they write code and know the cloud, so Python, Go, AWS IAM and the scanners sit in the top third of a minimal black and grey page.
Second choice: Catalyst. Catalyst skips the summary and leads with the current role under teal headings; choose it at staff level, when one job tells the whole story.
What goes in each section, in FAANGPath's order
FAANGPath prints its sections in a fixed order, the same in the PDF and the Word file. Here is that order for this sample, and what to put in each section.
- Professional Summary. Say which kind of security engineer you are (application, cloud, detection, infrastructure) and how you work: building controls into pipelines reads differently from running audits. Add CISSP or another credential at the end if the employer cares, since FAANGPath prints certifications last.
- Skills. Lead Technical with the security disciplines and the languages you write; many security engineering interviews include code review or a coding exercise. Put scanners, cloud security services and IaC under Tools, spelled the way the vendors spell them.
- Work Experience. Security work is easy to describe as activity ("performed reviews"). Write outcomes instead: findings fixed and how fast, risky patterns made impossible, accounts or repositories covered. Name one control you designed and the attack it stops.
- Education. One line after experience. A computer science degree is common but not required; the controls you shipped carry the page.
- Certifications. Give the full name and the year. ISC2 asks for five years of cumulative paid work in at least two of the eight CISSP domains (a relevant degree or an approved credential can count for one year); if you passed without that, you are an Associate of ISC2, so write that instead.
The sample resume as text
The same content as the files above, so you can copy a line or compare it with your own.
Sofia Petrova
Senior Security Engineer, Cloud and Application Security (CISSP)
Arlington, VA | sofia.petrova@example.com | (703) 555-0186 | github.com/sample-sofia-petrova | linkedin.com/in/sample-sofia-petrova
Security engineer with eight years in application and cloud security, the last four at a telehealth company on AWS. Builds controls into pipelines and infrastructure rather than auditing after release: scanning in CI, least-privilege IAM, threat models for new features. CISSP.
Experience
Senior Security Engineer, Quarry Hill Health, Arlington, VA (04/2022 to Present)
- Built the security stage of CI for 90 repositories (static analysis, dependency and container scanning, secret detection) with findings routed to the owning team; median time to fix a critical finding fell from 40 days to 6.
- Replaced long-lived AWS access keys with SSO and short-lived roles across 25 accounts, and wrote the service control policies that block public S3 buckets.
- Run threat modeling sessions with product engineers for new features; the video visit redesign shipped with session token binding that came out of the model.
- Coordinate the yearly external penetration test: scope, triage of findings and verification of each fix.
- Wrote the leaked-credential runbook and ran two tabletop exercises with the engineering on-call rotation.
Application Security Engineer, Northgate Payments, Reston, VA (07/2018 to 03/2022)
- Reviewed designs and Java code for the card vault and tokenization services.
- Started a security champions program and trained 14 engineers to triage scanner findings in their own teams.
- Closed a class of broken object-level authorization bugs in the merchant API by moving the checks into shared middleware.
Education
BS, Computer Science, Potomac Ridge University (05/2018)
Certifications
- Certified Information Systems Security Professional (CISSP), ISC2 (2023)
Skills
Application security, Threat modeling (STRIDE), AWS IAM and SCPs, Secure code review, Python, Go, OWASP Top 10, Semgrep, Trivy, GitHub Advanced Security, AWS Security Hub, Terraform, Burp Suite, Security champions programs, Writing standards engineers follow
How to make the sample yours
Shape the headline around your specialty
"Cloud and Application Security" in the sample tells the reader which half of security you sit in. Change it to detection engineering, identity or product security if that is your work.
Turn findings into fix times
The sample cuts the median time to fix a critical finding from 40 days to 6. Your ticketing and scanner dashboards hold the same figures, and a time-to-fix trend says more than a count of findings.
Name a control that removes a class of bug
Shared authorization middleware, a policy blocking public buckets, a lint rule for unsafe deserialization. Engineers who remove whole classes of risk are the ones security leads want to hire.
Show how you work with developers
Security champions, office hours, threat model sessions. A security engineer who cannot get other teams to ship fixes is stuck, and hiring managers probe for this.
Separate exercises from real incidents
Tabletop exercises are useful and worth a bullet, but label them as exercises. Write real incident work with your role in it.
Keywords to keep where they are true
Terms this kind of resume is usually searched for. Use the posting's exact wording, and only for work you have done.
- security engineering
- application security
- cloud security
- threat modeling
- secure code review
- SAST
- software composition analysis
- secrets management
- AWS IAM
- least privilege
- OWASP Top 10
- DevSecOps
- vulnerability management
- incident response
- CISSP
Mistakes to avoid
- Compliance frameworks you have only read about, listed as experience.
- Bullets about reviews and scans with no outcome attached.
- Details of vulnerabilities in a past employer's systems that are not fixed or public.
- Taking credit for penetration test findings. The testers found them; say what you triaged and fixed.
How the sample PDF reads in text extractors
We exported this sample with Resumity's PDF exporter in Chrome on 2026-10-29 and read the file back with three open-source text extractors. This shows whether software that turns a PDF into text can recover it; it is not a test of any commercial applicant tracking system. How we test templates.
| Extractor | Name, email, phone | Headings | Bullets intact |
|---|---|---|---|
| pdf.js 4.10.38 | All found | 5 of 5 | 8 of 8 |
| pdftotext (Xpdf) 4.00 | All found | 5 of 5 | 8 of 8 |
| pypdf 6.13.0 | All found | 5 of 5 | 8 of 8 |
Frequently asked questions
Do I need a CISSP to work as a security engineer?
No, though some postings ask for it. ISC2 requires five years of relevant paid experience for the full credential, so early-career engineers often hold Associate of ISC2 or a cloud security certificate instead.
How much coding should a security engineer resume show?
Enough to prove you can ship a fix or a control yourself: a language in the skills rows and at least one bullet where you wrote the code, such as shared middleware or a scanner integration.
How do I describe vulnerabilities without exposing my employer?
Name the class and the fix, not the system. "Closed a class of broken object-level authorization bugs in a merchant API" is specific enough to discuss in an interview and reveals nothing exploitable.
Which OWASP Top 10 should I refer to?
Name the edition you work from. OWASP lists the 2025 edition as the current release, with 2021 and 2017 as earlier versions; a plain "OWASP Top 10" is fine in a skills row.
How do I move from SOC analyst to security engineer?
Show the building you already do: detections written as code, automation in Python, a control you proposed and shipped with another team. Change the headline only when the bullets support it.
Will applicant tracking systems read this FAANGPath PDF?
The sample PDF read back with its contact details, all 5 section headings and all 8 bullets intact in three open-source text extractors (pdf.js, pdftotext and pypdf). Commercial systems such as Workday, Greenhouse or Taleo were not tested, and each employer configures its own.
Guides and templates for this resume
Sources, checked 29 October 2026
We opened every page below on that date. Pay, rules and requirements change, so check the source before you rely on a detail.
- ISC2: CISSP experience requirements (five years of cumulative full-time experience in two or more of the eight domains; a degree or an approved credential can satisfy one year; otherwise Associate of ISC2)
- OWASP Foundation: OWASP Top Ten (the most current released version is the OWASP Top 10 2025; 2021 and 2017 are earlier editions)
More in resume templates by job title.