Resume template · Updated October 2026
Incident response analyst resume template
Short answer
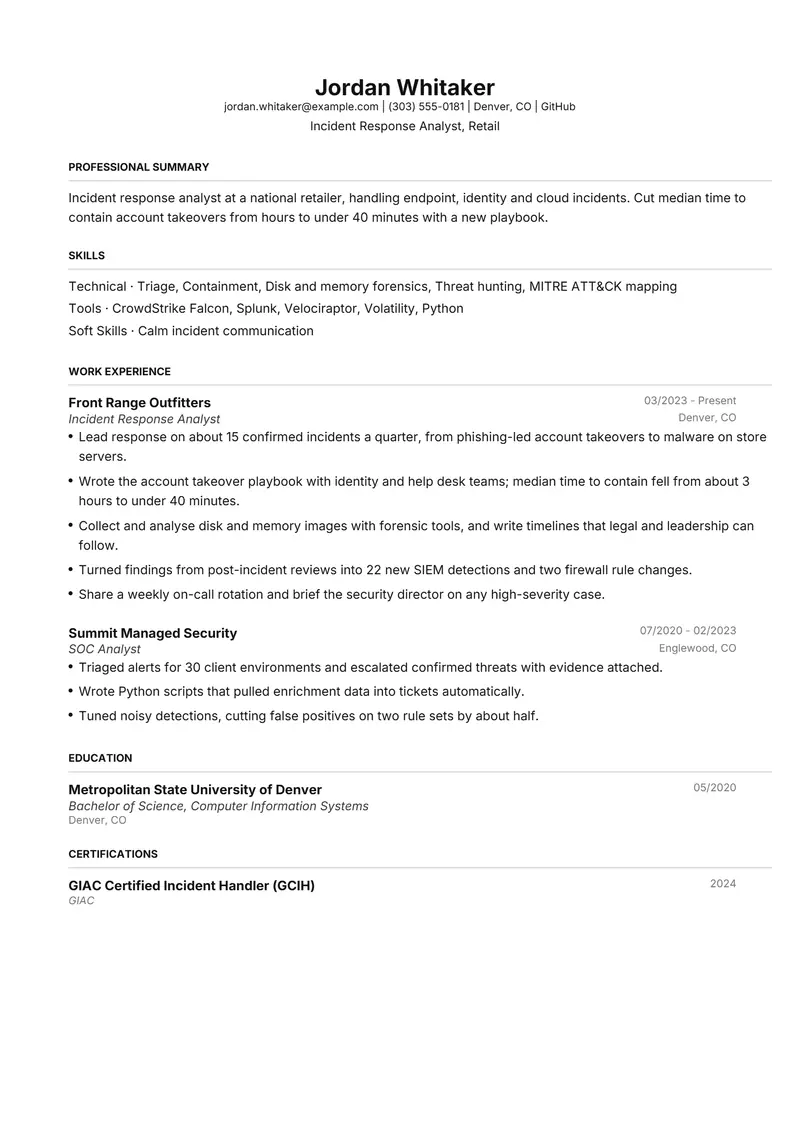
FAANGPath fits incident response: it prints skills before jobs, so the detection tools, forensic tools and scripting that IR roles screen for are read first, followed by incidents handled and playbooks written. The fictional sample moved from a SOC into an incident response team at a retailer. Describe incidents by type and outcome only, never by name, and replace the sample's numbers with your own.
Download the incident response analyst sample
Jordan is a fictional incident response analyst. Replace every detail with your own before you send it.
The files are made in your browser by Resumity's own exporters, from this sample. The builder opens it as your own resume: click any line to replace it. Free plan, no watermark.
Why FAANGPath suits an incident response analyst resume
FAANGPath prints a short summary, labelled skills rows and then experience, in black and grey with full-width heading rules. Incident response postings filter on tools such as EDR, SIEM and forensics suites, so the skills rows answer that before the reader reaches the jobs.
Second choice: Meridian. Meridian has the same skills-first order with grey rules beside the headings, a near match if you prefer its centred header.
What goes in each section, in FAANGPath's order
FAANGPath prints its sections in a fixed order, the same in the PDF and the Word file. Here is that order for this sample, and what to put in each section.
- Professional Summary. Your IR role (responder, lead, forensic analyst), the environment (cloud, endpoints, retail, finance) and one measure such as incidents handled or time to contain.
- Skills. Rows for detection and response tools, forensics, scripting and frameworks. Keep each row to what you have used on real incidents.
- Work Experience. Bullets by phase: triage, containment, investigation, recovery, lessons learned. Say what changed afterwards, such as a new detection or a closed gap.
- Education. Degree with the year, or the training route that brought you in if you have no degree.
- Certifications. Security and forensics certifications with the issuer and year. FAANGPath prints these after education, so name the main one in the summary.
The sample resume as text
The same content as the files above, so you can copy a line or compare it with your own.
Jordan Whitaker
Incident Response Analyst, Retail
Denver, CO | jordan.whitaker@example.com | (303) 555-0181 | github.com/sample-jordan-whitaker
Incident response analyst at a national retailer, handling endpoint, identity and cloud incidents. Cut median time to contain account takeovers from hours to under 40 minutes with a new playbook.
Experience
Incident Response Analyst, Front Range Outfitters, Denver, CO (03/2023 to Present)
- Lead response on about 15 confirmed incidents a quarter, from phishing-led account takeovers to malware on store servers.
- Wrote the account takeover playbook with identity and help desk teams; median time to contain fell from about 3 hours to under 40 minutes.
- Collect and analyse disk and memory images with forensic tools, and write timelines that legal and leadership can follow.
- Turned findings from post-incident reviews into 22 new SIEM detections and two firewall rule changes.
- Share a weekly on-call rotation and brief the security director on any high-severity case.
SOC Analyst, Summit Managed Security, Englewood, CO (07/2020 to 02/2023)
- Triaged alerts for 30 client environments and escalated confirmed threats with evidence attached.
- Wrote Python scripts that pulled enrichment data into tickets automatically.
- Tuned noisy detections, cutting false positives on two rule sets by about half.
Education
Bachelor of Science, Computer Information Systems, Metropolitan State University of Denver (05/2020)
Certifications
- GIAC Certified Incident Handler (GCIH), GIAC (2024)
Skills
Triage, Containment, Disk and memory forensics, Threat hunting, MITRE ATT&CK mapping, CrowdStrike Falcon, Splunk, Velociraptor, Volatility, Python, Calm incident communication
How to make the sample yours
Describe incidents by type, not name
Phishing-led account takeover, ransomware on a file server, cloud key exposure. Type and scale tell a reader what you can handle without revealing anything confidential.
Show time to contain
Hours or minutes from alert to containment, before and after a playbook or tooling change. It is the outcome IR leads care about most.
Turn lessons learned into bullets
A new detection rule, a hardened configuration, an access change after an incident. What changed afterwards proves the response improved the company.
Mention on-call and communication
Rotations, briefings to executives or legal, coordination with outside responders. IR is as much coordination as technical work.
Keywords to keep where they are true
Terms this kind of resume is usually searched for. Use the posting's exact wording, and only for work you have done.
- incident response
- digital forensics
- triage
- containment
- EDR
- SIEM
- threat hunting
- malware analysis
- playbooks
- root cause analysis
- MITRE ATT&CK
- Python
Mistakes to avoid
- Naming a breached company or quoting data from a real incident.
- Tool lists with no incident work behind them.
- Skipping what changed after each incident.
- Inflating your role in an incident led by someone else.
How the sample PDF reads in text extractors
We exported this sample with Resumity's PDF exporter in Chrome on 2026-10-29 and read the file back with three open-source text extractors. This shows whether software that turns a PDF into text can recover it; it is not a test of any commercial applicant tracking system. How we test templates.
| Extractor | Name, email, phone | Headings | Bullets intact |
|---|---|---|---|
| pdf.js 4.10.38 | All found | 5 of 5 | 8 of 8 |
| pdftotext (Xpdf) 4.00 | All found | 5 of 5 | 8 of 8 |
| pypdf 6.13.0 | All found | 5 of 5 | 8 of 8 |
Frequently asked questions
How do I describe incidents without breaking confidentiality?
Use the incident type, scale and outcome, and leave out names, dates and anything that could identify the company or people. Your employer's policy on public statements takes priority.
Can I move into incident response from a SOC role?
Yes, it is a common path. Show escalations you investigated end to end, any forensic work, and scripts or detections you wrote, and put them high in the SOC job's bullets.
Should I list home lab work?
If your professional incident experience is thin, a short projects line about lab investigations helps. Keep it below real incidents and say plainly it was a lab.
How long should an incident response resume be?
One page for most analysts. Leads with several years of incidents and tool rollouts can use two pages.
Will applicant tracking systems read this FAANGPath PDF?
The sample PDF read back with its contact details, all 5 section headings and all 8 bullets intact in three open-source text extractors (pdf.js, pdftotext and pypdf). Commercial systems such as Workday, Greenhouse or Taleo were not tested, and each employer configures its own.
Guides and templates for this resume
More in resume templates by job title.