Resume template · Updated October 2026
Cybersecurity resume template
Short answer
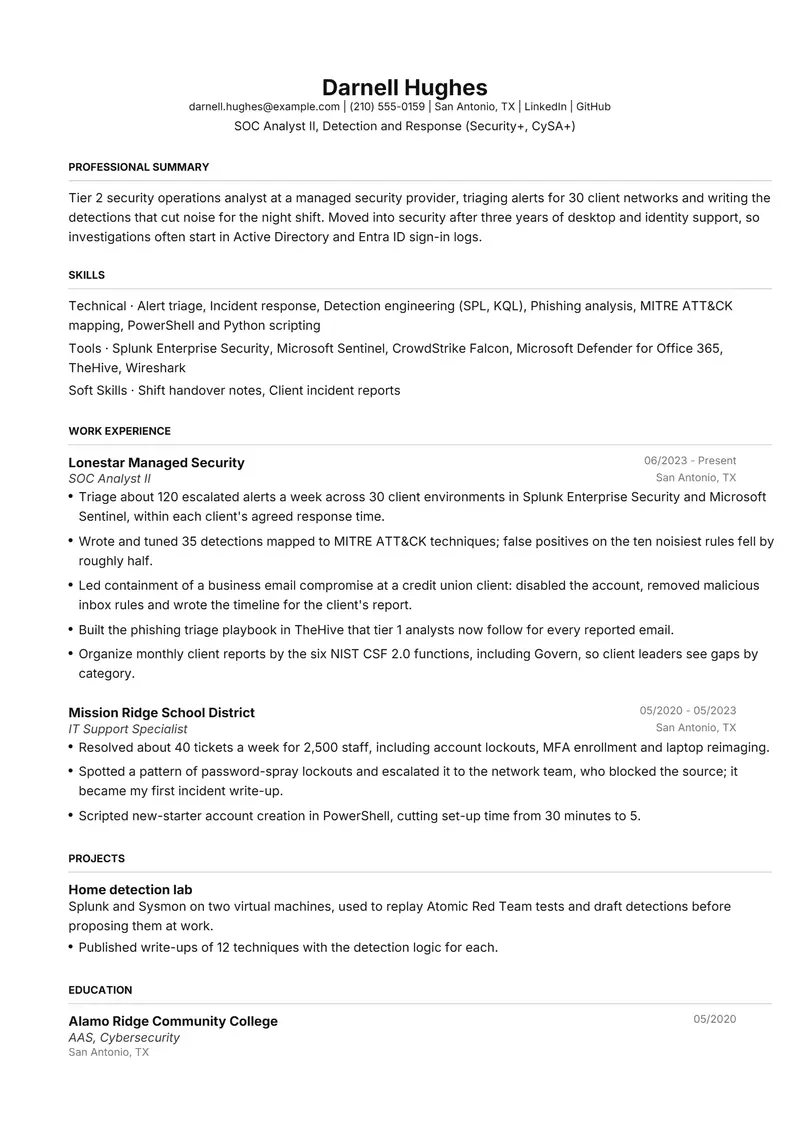
FAANGPath suits most cybersecurity resumes because its labelled skill rows, naming the SIEM, EDR, scripting and frameworks, print before any job. That matters when your title history starts at a help desk. The fictional sample is a tier 2 SOC analyst in San Antonio who came up from school district IT support, with alert triage, detections mapped to MITRE ATT&CK, a phishing playbook and two CompTIA certifications.
Download the cybersecurity sample
Darnell is a fictional SOC analyst II. Replace every detail with your own before you send it.
The files are made in your browser by Resumity's own exporters, from this sample. The builder opens it as your own resume: click any line to replace it. Free plan, no watermark.
Why FAANGPath suits a cybersecurity resume
FAANGPath is meant for technical candidates who want their tools read before their jobs, and security hiring leans hard on named tooling: the SIEM, the EDR platform, the scripting language and the frameworks you map work to. Its labelled rows put Splunk, CrowdStrike and MITRE ATT&CK above a work history that may still open with an IT support title.
Second choice: Meridian. Meridian also prints skills before experience on a colourless page, with a colon after each label and grey rules beside the headings.
What goes in each section, in FAANGPath's order
FAANGPath prints its sections in a fixed order, the same in the PDF and the Word file. Here is that order for this sample, and what to put in each section.
- Professional Summary. Say which part of security you work in (operations, engineering, governance and risk, or offensive testing) and how many systems or clients you cover. Security teams are small and specialised, so "cybersecurity professional" tells a hiring manager nothing about where you would sit.
- Skills. Three rows: methods (triage, detection writing, forensics, risk assessment), named tools (SIEM, EDR, email security, case management), and frameworks you map work to, such as MITRE ATT&CK for detections or NIST CSF 2.0 and ISO/IEC 27001 for governance. Write "Splunk Enterprise Security", not "SIEM tools"; product names are what get searched.
- Work Experience. Each bullet needs a count and a consequence: alerts handled, detections written, incidents contained, vulnerabilities closed, audit findings resolved. Describe incidents by type and your part in them, never by client name or with details an attacker could use.
- Projects. A home lab, capture-the-flag results or published write-ups fill the gap when paid security experience is short. Say what you built and what you learned to detect with it.
- Education. An associate degree in cybersecurity, a computer science degree or no degree at all: the field hires plenty of people from help desks and the military. One line is enough.
- Certifications. FAANGPath prints these last, so repeat the one the posting asks for in your headline. CompTIA lists Security+ as valid for three years, renewed through continuing education. CISSP needs five years of cumulative full-time work in at least two of its eight domains; pass the exam before that and you are an Associate of ISC2.
The sample resume as text
The same content as the files above, so you can copy a line or compare it with your own.
Darnell Hughes
SOC Analyst II, Detection and Response (Security+, CySA+)
San Antonio, TX | darnell.hughes@example.com | (210) 555-0159 | linkedin.com/in/sample-darnell-hughes | github.com/sample-darnell-hughes
Tier 2 security operations analyst at a managed security provider, triaging alerts for 30 client networks and writing the detections that cut noise for the night shift. Moved into security after three years of desktop and identity support, so investigations often start in Active Directory and Entra ID sign-in logs.
Experience
SOC Analyst II, Lonestar Managed Security, San Antonio, TX (06/2023 to Present)
- Triage about 120 escalated alerts a week across 30 client environments in Splunk Enterprise Security and Microsoft Sentinel, within each client's agreed response time.
- Wrote and tuned 35 detections mapped to MITRE ATT&CK techniques; false positives on the ten noisiest rules fell by roughly half.
- Led containment of a business email compromise at a credit union client: disabled the account, removed malicious inbox rules and wrote the timeline for the client's report.
- Built the phishing triage playbook in TheHive that tier 1 analysts now follow for every reported email.
- Organize monthly client reports by the six NIST CSF 2.0 functions, including Govern, so client leaders see gaps by category.
IT Support Specialist, Mission Ridge School District, San Antonio, TX (05/2020 to 05/2023)
- Resolved about 40 tickets a week for 2,500 staff, including account lockouts, MFA enrollment and laptop reimaging.
- Spotted a pattern of password-spray lockouts and escalated it to the network team, who blocked the source; it became my first incident write-up.
- Scripted new-starter account creation in PowerShell, cutting set-up time from 30 minutes to 5.
Projects
Home detection lab: Splunk and Sysmon on two virtual machines, used to replay Atomic Red Team tests and draft detections before proposing them at work.
- Published write-ups of 12 techniques with the detection logic for each.
Education
AAS, Cybersecurity, Alamo Ridge Community College (05/2020)
Certifications
- CompTIA Security+, CompTIA (2024)
- CompTIA CySA+, CompTIA (2025)
Skills
Alert triage, Incident response, Detection engineering (SPL, KQL), Phishing analysis, MITRE ATT&CK mapping, PowerShell and Python scripting, Splunk Enterprise Security, Microsoft Sentinel, CrowdStrike Falcon, Microsoft Defender for Office 365, TheHive, Wireshark, Shift handover notes, Client incident reports
How to make the sample yours
Pick your lane in the headline
SOC analyst, security engineer, GRC analyst and penetration tester are read very differently. Write the one you are applying for, plus the certification that matches it, in the line under your name.
Translate the IT job underneath
Account lockouts, MFA rollouts, patching, firewall changes and phishing reports from staff are security work done under an IT title. Move those bullets to the top of the older role, as the sample does with its password-spray catch.
Measure detections, not alerts closed
Closing many alerts can just mean a noisy SIEM. Rules you wrote, false positives you removed and the time it took to contain a real incident show judgement.
State a clearance exactly as it stands
For US government and defence contractor roles, write the level and whether it is active, such as "Active Secret clearance". If you are unsure of its status after leaving an employer, check before listing it.
Keep incident details safe
Name the incident type (business email compromise, ransomware precursor, exposed storage bucket) and your role in it. Leave out client names, hostnames and anything that explains how a defence works.
Keywords to keep where they are true
Terms this kind of resume is usually searched for. Use the posting's exact wording, and only for work you have done.
- security operations
- incident response
- SIEM
- Splunk
- Microsoft Sentinel
- EDR
- threat detection
- MITRE ATT&CK
- NIST CSF
- vulnerability management
- phishing analysis
- log analysis
- Security+
- PowerShell
- Python
Mistakes to avoid
- Listing every tool from a training course (Metasploit, Nmap, Burp Suite, Kali) for a defensive role in which you have never used them.
- Putting "CISSP" or "CISSP candidate" after your name before you hold it. If you passed the exam without the experience, Associate of ISC2 is the accurate term.
- Naming breached clients or describing internal security gaps in detail.
- "Monitored the network" as a bullet. Say what you watched with, how many alerts, and what you did when one turned out to be real.
How the sample PDF reads in text extractors
We exported this sample with Resumity's PDF exporter in Chrome on 2026-10-29 and read the file back with three open-source text extractors. This shows whether software that turns a PDF into text can recover it; it is not a test of any commercial applicant tracking system. How we test templates.
| Extractor | Name, email, phone | Headings | Bullets intact |
|---|---|---|---|
| pdf.js 4.10.38 | All found | 6 of 6 | 9 of 9 |
| pdftotext (Xpdf) 4.00 | All found | 6 of 6 | 9 of 9 |
| pypdf 6.13.0 | All found | 6 of 6 | 9 of 9 |
Frequently asked questions
How do I move from IT support into cybersecurity on paper?
Lead with the security parts of your support job (identity, MFA, patching, phishing reports, endpoint tools), add a certification such as Security+, and show a lab or write-up that proves you can investigate. Put the security role you want in the headline.
Do I need a certification to get a cybersecurity job?
Not always, but many entry-level and government postings ask for one, and Security+ is a common first choice. Experience counts for more as you progress; CISSP itself expects five years of relevant work.
Should I list my security clearance?
Yes, for roles that require one: give the level and whether it is active. For jobs where it is irrelevant, it can stay off; it is a status, not a skill.
How much should a security resume say about incidents?
Enough to show your role and the outcome (contained within hours, no data lost, a process changed), and not enough to identify the organisation or reveal how its defences work.
Does governance, risk and compliance work count as cybersecurity experience?
Yes. Risk assessments, policy writing, audits against ISO/IEC 27001 and control mapping to NIST CSF are a recognised part of the field, and Security and Risk Management is one of the eight CISSP domains.
Will applicant tracking systems read this FAANGPath PDF?
The sample PDF read back with its contact details, all 6 section headings and all 9 bullets intact in three open-source text extractors (pdf.js, pdftotext and pypdf). Commercial systems such as Workday, Greenhouse or Taleo were not tested, and each employer configures its own.
Guides and templates for this resume
- IT Support Resume Example and Writing Guide
- How to List Certifications and Licenses on a Resume
- Federal Resume Example and USAJOBS Format Guide
- Military to Civilian Resume: How to Translate Your Service for Employers
- Cloud computing resume template
- Technical Skills for a Resume: What Counts and How to List Them
Sources, checked 29 October 2026
We opened every page below on that date. Pay, rules and requirements change, so check the source before you rely on a detail.
- NIST: NIST Releases Version 2.0 of Landmark Cybersecurity Framework (CSF 2.0 released 26 February 2024; six functions Identify, Protect, Detect, Respond, Recover and the new Govern)
- ISC2: CISSP Experience Requirements (five years cumulative full-time experience in two or more of eight domains; Associate of ISC2 if the exam is passed without it)
- CompTIA: Certification Renewal Policy (Security+ valid for three years from certification, renewable through continuing education)
- MITRE: MITRE ATT&CK (a knowledge base of adversary tactics and techniques based on real-world observations)
More in resume templates by industry.